
- Monthly visits
- 673
- 2026-09
- Monthly growth +82.4%
VibeZero - Scan AI-built apps and verify fixes before release
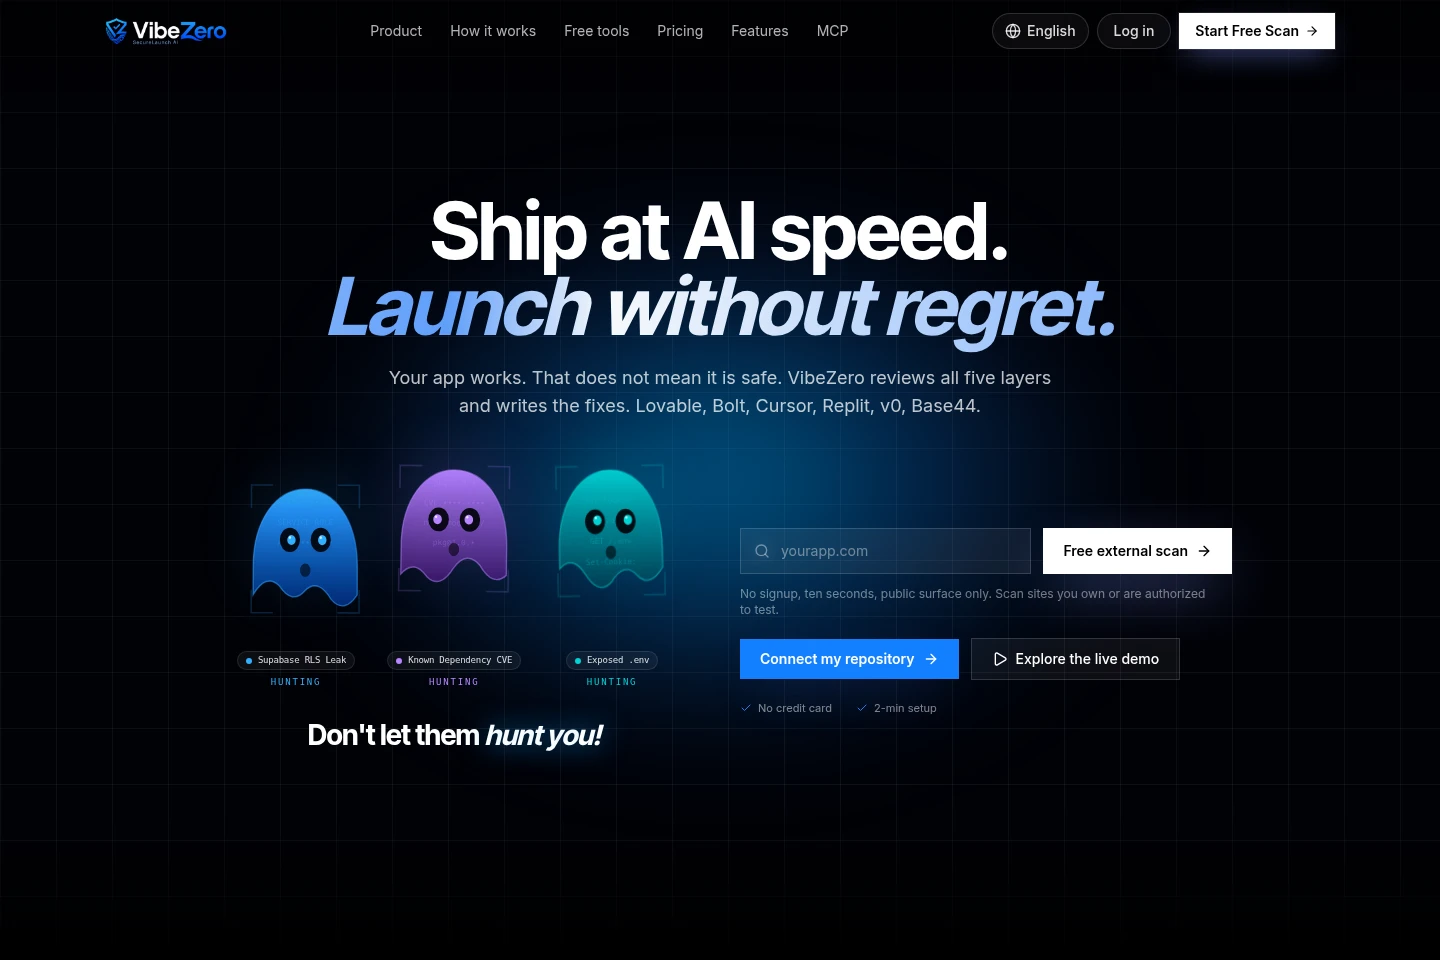
VibeZero scans AI-built applications across code, dependencies, secrets, configuration, and the running app. It combines findings into a launch-readiness score, creates AI-assisted fix tasks, and verifies fixes with a rescan. Teams can connect a repository through the GitHub app or CLI; a separate free external scan checks a site's public surface.
- AI Coding
- Security Scanners
- AI app security scanner
- vibe coding security
- release readiness scan
Capabilities
Five-layer security scan
Scans code, dependencies, secrets, configuration, and the running application, then outputs security findings. Connect a repository using the GitHub app or CLI; the scan also includes the deployed app.
Launch readiness score
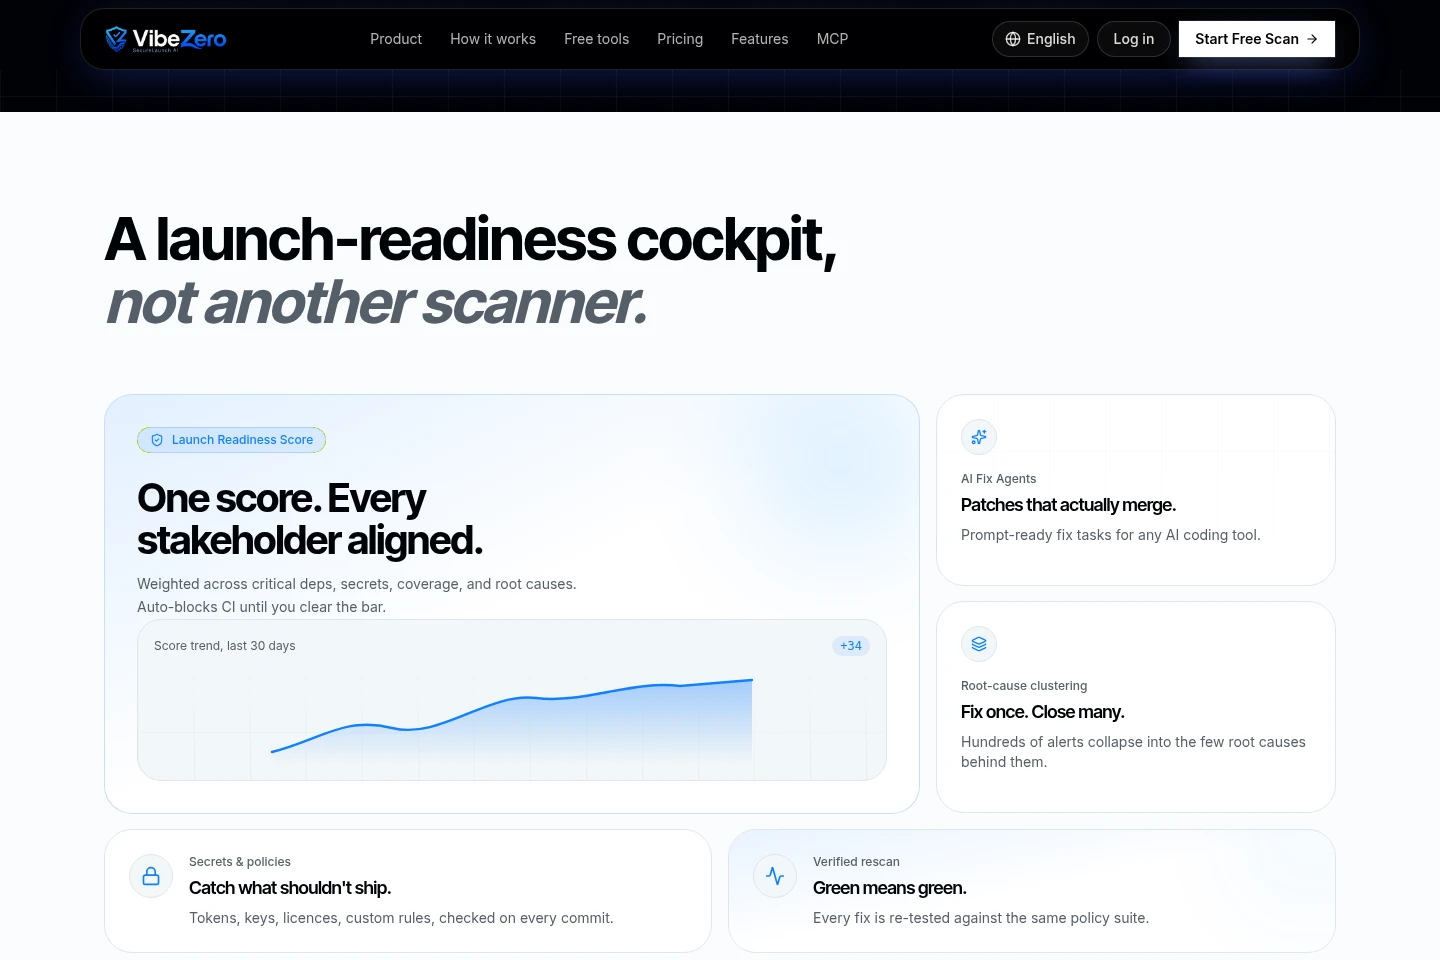
Combines risk drivers into a weighted score from 0 to 100 and a release decision. The score considers dependencies, secrets, coverage, and root causes, and can be used to gate CI.
AI fix tasks
Creates prompt-ready tasks and patches for identified findings. Teams can hand tasks to AI coding tools, and a fix is marked verified only after a rescan confirms it.
Free external scan
Checks a website's public surface and outputs results for page content, loaded scripts, and its certificate. It requires no signup, is limited to public-surface checks, and is intended for sites the user owns or is authorized to test.
Pricing
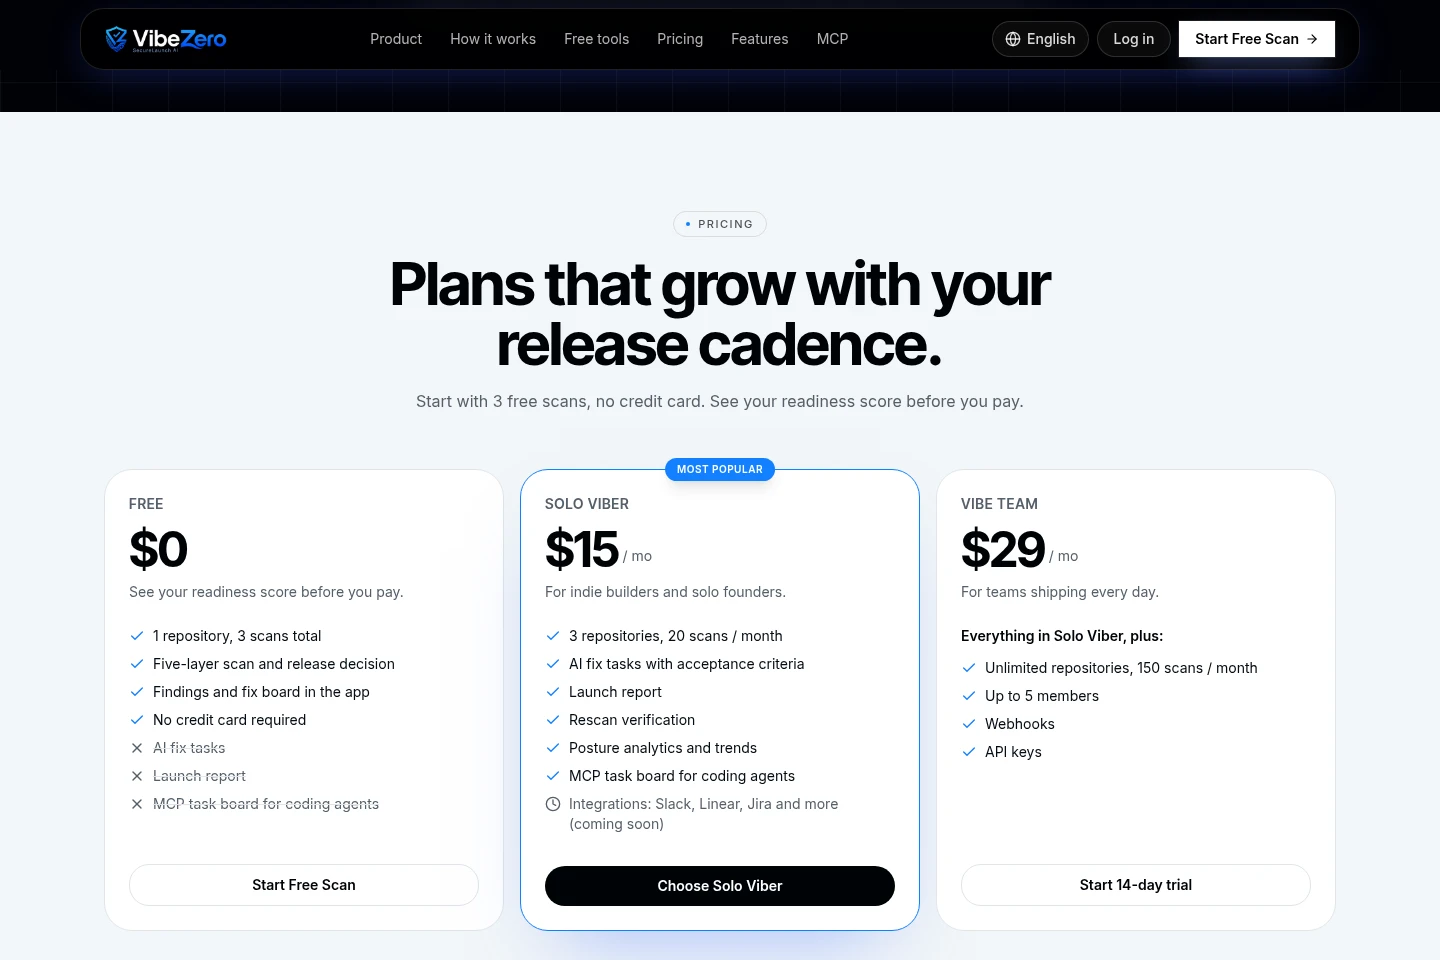
VibeZero offers a free plan and describes a custom plan; the free option starts with three scans. Compare scan access and the team or agency features offered on a custom plan when choosing.
| Plan | Price | Included features and limits |
|---|---|---|
| Free | $0 |
|
| Custom | Custom pricing; contact sales |
|
Use cases
Review an AI-built app before release
When a team is preparing an AI-built application for release, connect its repository through the GitHub app or CLI and run a scan across code, dependencies, secrets, configuration, and the deployed app. Use the launch score and release decision to review blockers.
Prioritize and track security fixes
When a scan returns many findings, use severity summaries and root-cause clustering to identify release blockers. Generate fix tasks, hand prompt-ready patches to a coding tool, and rescan to verify completed fixes.
Check a website's public security surface
When checking a site without connecting a repository, enter its web address for the free external scan. It checks the page, loaded scripts, and certificate without signup; use it only for a site you own or are authorized to test.
Limitations
The free external scan checks only a site's public surface; it does not inspect the repository or establish launch readiness.
The external scan is for sites the user owns or is authorized to test.
Workflow integrations beyond the GitHub app are described as coming soon; they are not available integrations in the supplied evidence.
Who it is for
Developers building applications with AI coding tools who need security findings and fix tasks before release
Security teams that need a launch threshold, release blockers, and rescan-verified fixes across repositories
Agencies managing security baselines and release checks for multiple client applications
FAQ
What does the full VibeZero scan inspect?
It inspects five layers: code, dependencies, secrets, configuration, and the running app. The connected-repository scan includes the repository, lockfiles and history, as well as the deployed application.
How is the free external scan different from a repository scan?
The external scan checks a site's public surface, including its page, loaded scripts, and certificate, without signup. It cannot see the site's code and is held at 84 out of 100, so it cannot declare an app launch-ready.
When is a fix marked verified?
A fix is marked verified only after a rescan confirms it against the same policy suite. A generated task or patch by itself does not count as verified.
Can VibeZero block a release?
Yes. The launch-readiness score can gate CI, and the workflow describes automatically blocking risky releases and unblocking CI once issues are cleared.
Which integrations are available now?
The GitHub app is connected today. The site describes other workflow integrations as in development or coming soon, so they should not be treated as currently available.
How can I get pricing for an agency or team?
Contact [email protected] for agency and team pricing, invoicing, procurement paperwork, or questions about repository coverage. The site also describes white-label reports, client management, per-client launch policies, SSO, and audit logs as available on a custom plan.
Comments